Android signing keys
Every Android build is signed with the app's key: let FluxNative create it or register your own, copy its fingerprints, and keep it safe.
Updated Oct 11, 2026
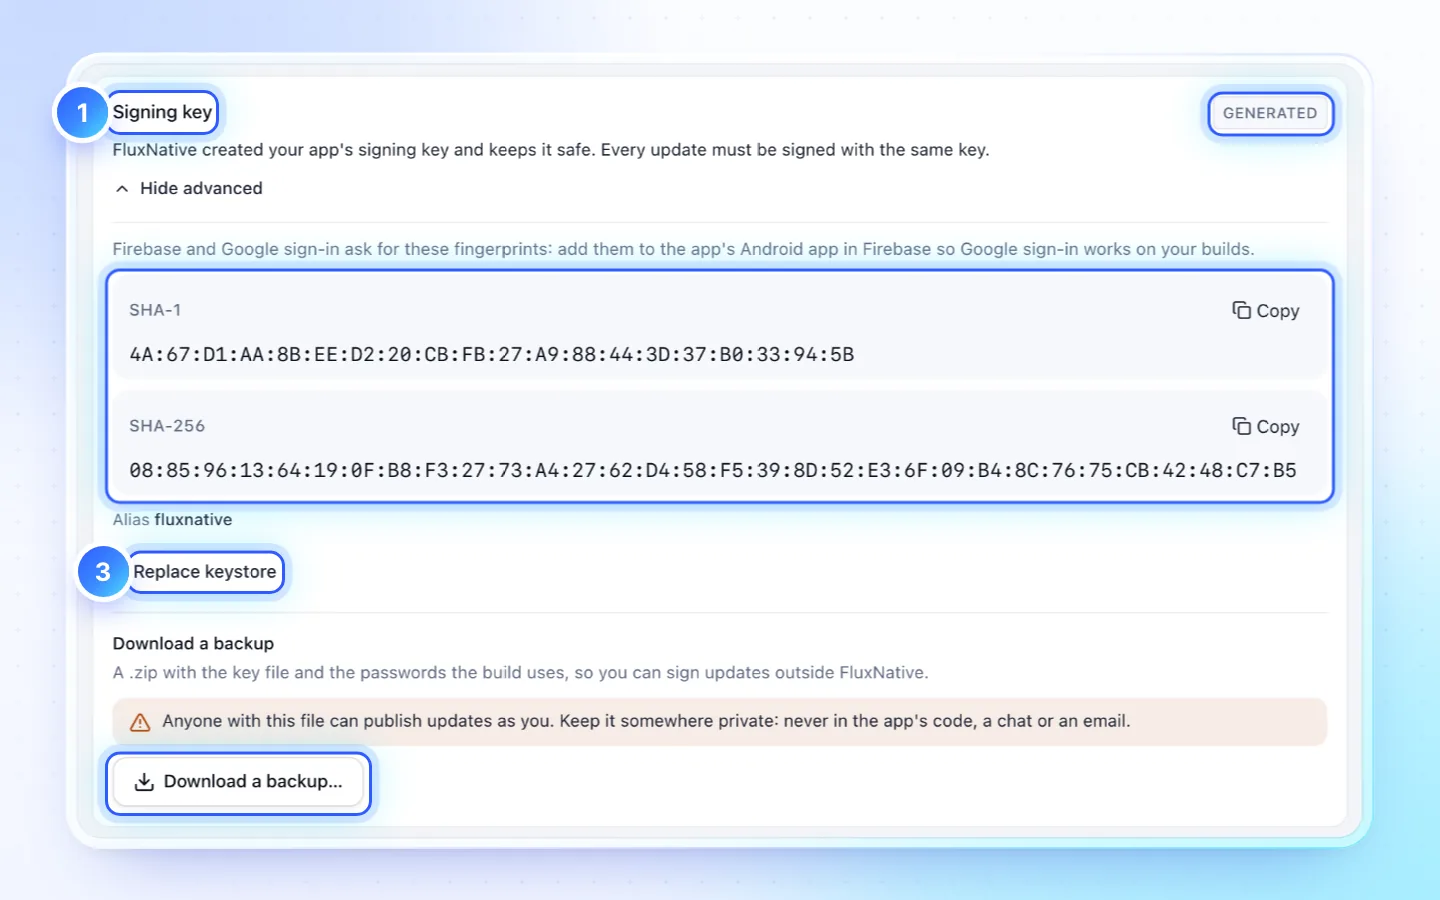
Create or register the key
- Click Build, choose Android, and find Signing key.
- New app: let the first build create the key, or click Create signing key now under Advanced.
- Already published with your own key: click Upload .jks under Advanced, before the first build.
- Enter the alias, the keystore password and the key password, then save.
SHA fingerprints
Advanced shows SHA-1 and SHA-256 with copy buttons. Add both to Firebase for Google sign-in; Google Maps needs the SHA-1. With Firebase connected, the assistant can add them, and the checks before a build flag missing ones.
Good to know
- Two keys sign an app on Google Play: this keystore is the upload key (the first App Bundle registers it), and Google re-signs Play installs with its app signing key. Add both SHA pairs to Firebase; Play's are in Play Console › Protected with Play › App signing.
- The owner can Download a backup (the
.jksand its passwords) under Advanced, after confirming their password. Downloads are listed in Team › Activity. - Replace keystore stops installed copies from updating, and Play rejects it unless Google arranged the change.
Related
Did this page help?